Inside the kit
See real pages from the material
These images were generated straight from the files you receive — nothing was mocked up or redrawn. Tap to enlarge.
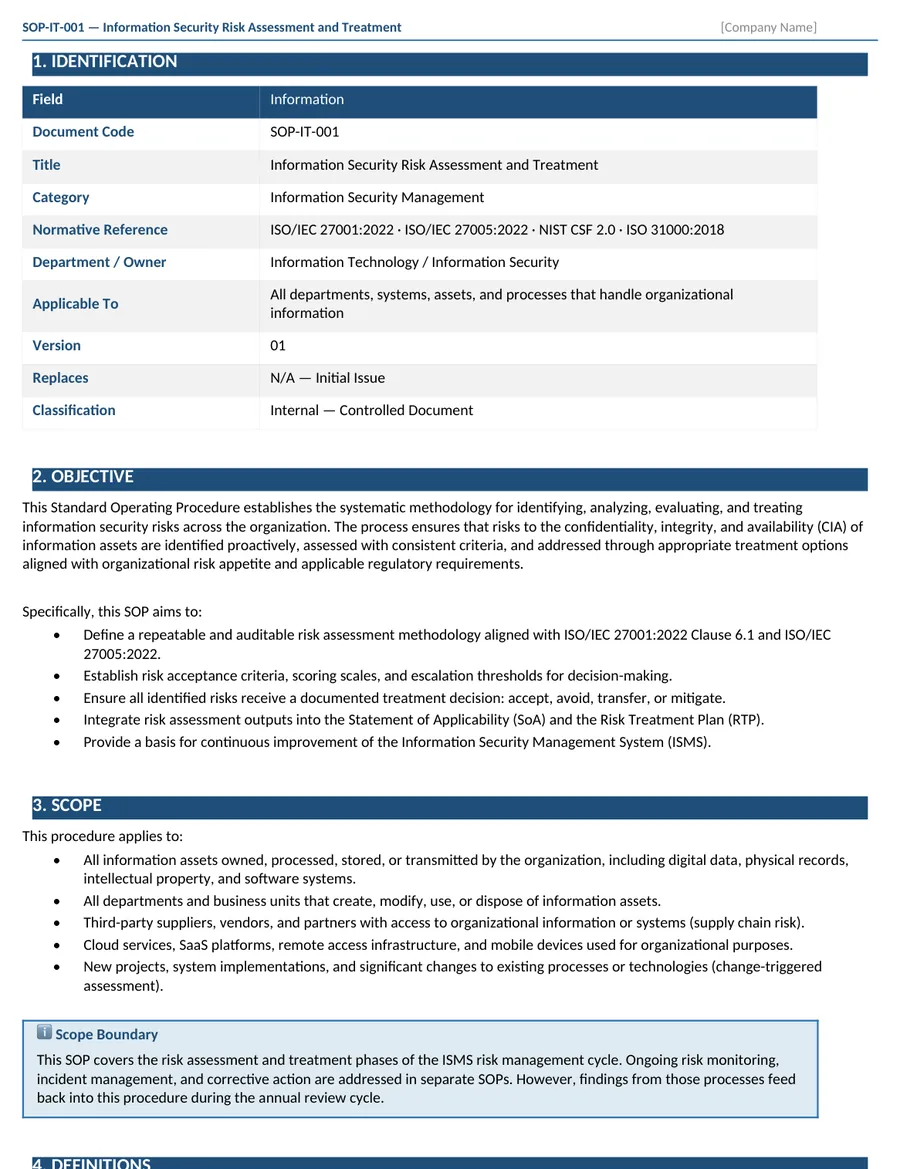
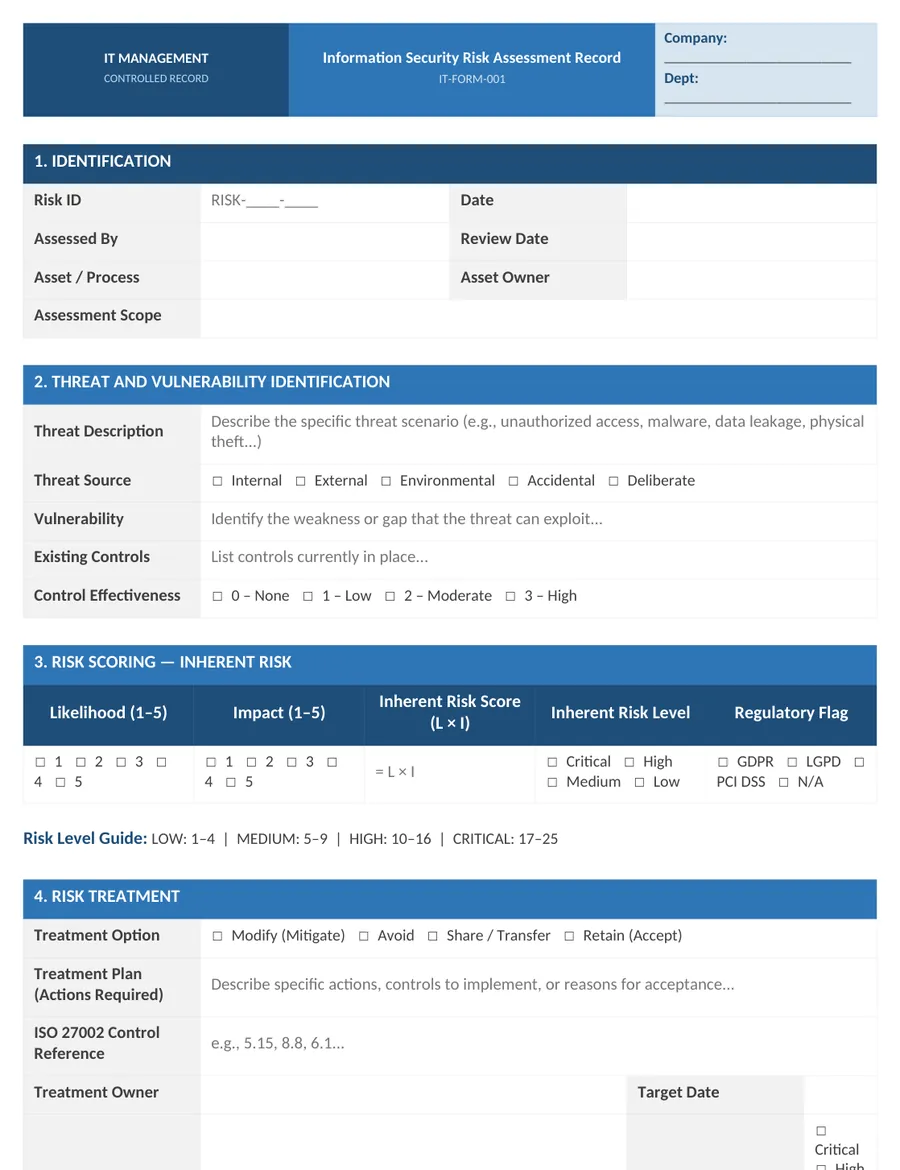
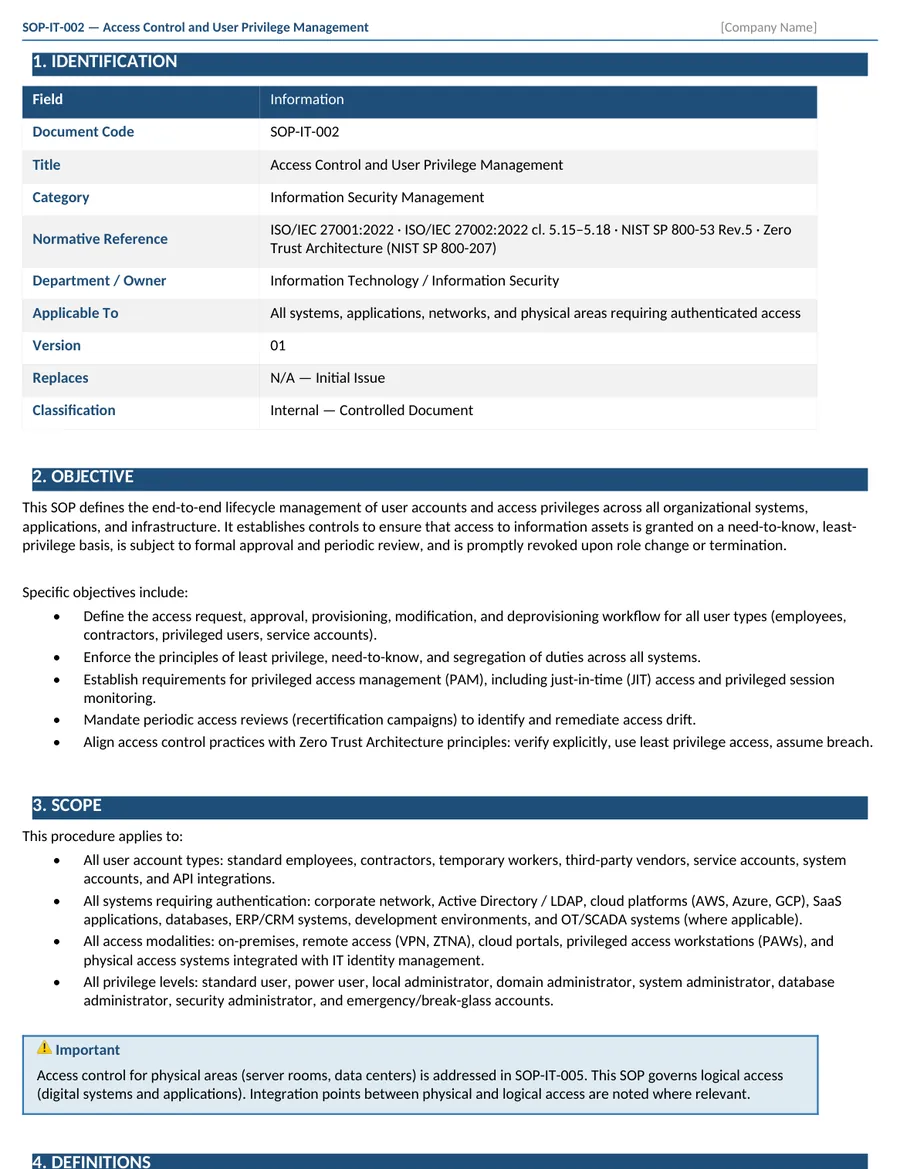
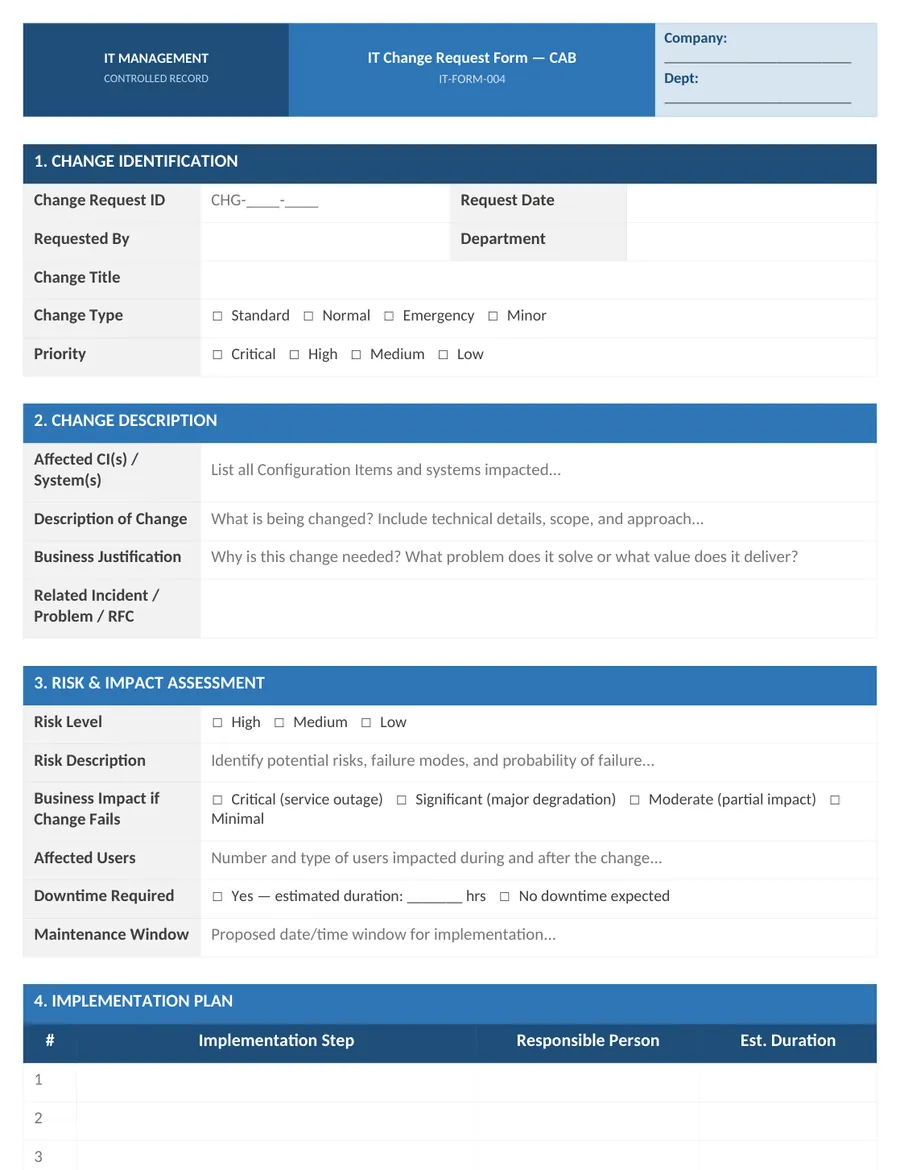
40 ready-to-use SOPs, 10 operational forms, Excel Dashboard, and Audit Checklist — everything your IT department needs to be audit-ready, in hours, not months.
Get the Complete Kit — $49When documentation gaps show up during an audit, the real damage isn't just a finding — it's the scramble, the overtime, and the risk that follows.
A single well-structured SOP takes 8–15 hours to research, write, review, and format. Multiply that by 40 procedures and your team loses months of productivity.
Missing or poorly written procedures are the #1 source of nonconformities in ISO 27001 audits. Each finding triggers corrective actions, follow-up audits, and management pressure.
Having a procedure is not enough — auditors demand evidence it's being followed. Without operational forms capturing each activity, you can't prove your ISMS is working.
Hiring a consultant to write 40 SOPs and 10 forms? Budget $18,000–$45,000. And you still need to customize everything to fit your organization.
Different authors, different formats, different depths. Without a unified standard across procedures and records, your ISMS looks fragmented — and auditors notice immediately.
Imagine receiving 40 professionally structured SOPs plus 10 ready-to-use operational forms — each designed to work together. Your procedures define the what; your forms capture the evidence.
Every SOP and every form is designed to solve a real operational problem — not just fill a compliance checkbox.
Every SOP maps directly to ISO 27001, ISO 27002, ISO 20000, and NIST controls. Pair them with the 10 forms and your auditor finds both the procedure and the evidence — exactly what they need.
Stop starting from a blank page. Open any file, add your company name and logo, adjust roles in the RACI matrix, and you have a production-ready procedure. Most teams are operational within a week.
A consultant charges $300–$800 per SOP, plus additional fees for forms. This kit gives you everything at a fraction of the cost — with the same depth and structure professionals deliver.
The 10 operational forms are directly linked to your SOPs. Each risk assessment, incident, or change request follows the same structure as the procedure that governs it — generating audit-ready records automatically.
One format, one structure, one vocabulary across 40 SOPs and 10 forms. When your department follows the same templates, handoffs become seamless and onboarding takes days instead of weeks.
Every file is a standard .docx or .xlsx — no locked PDFs. Edit in Word, Google Docs, or LibreOffice. Add your logo, adjust terminology, expand sections. Complete ownership, forever.
One purchase: all 40 SOPs, 10 operational forms, the Excel Dashboard and the Audit Checklist.
After payment, download all files immediately. No waiting, no drip content, no lessons to watch. This is not a course.
Open any file in Word or Google Docs. Add your logo, company name, adjust RACI roles, and tailor procedures and forms to your environment.
Use the SOPs to govern operations, the forms to capture evidence, and the Excel Dashboard to measure KPI performance — a complete cycle.
Seven thematic blocks — from information security to people management — so nothing falls through the cracks.
SOPs define the what and how. These forms are the evidence that your procedures are actually being followed — the piece that turns a good ISMS into an auditable one.
Threat identification, inherent risk scoring (L×I), treatment plan with ISO 27002 control references, residual risk calculation, GDPR/LGPD regulatory flag, and 3-level approval sign-off.
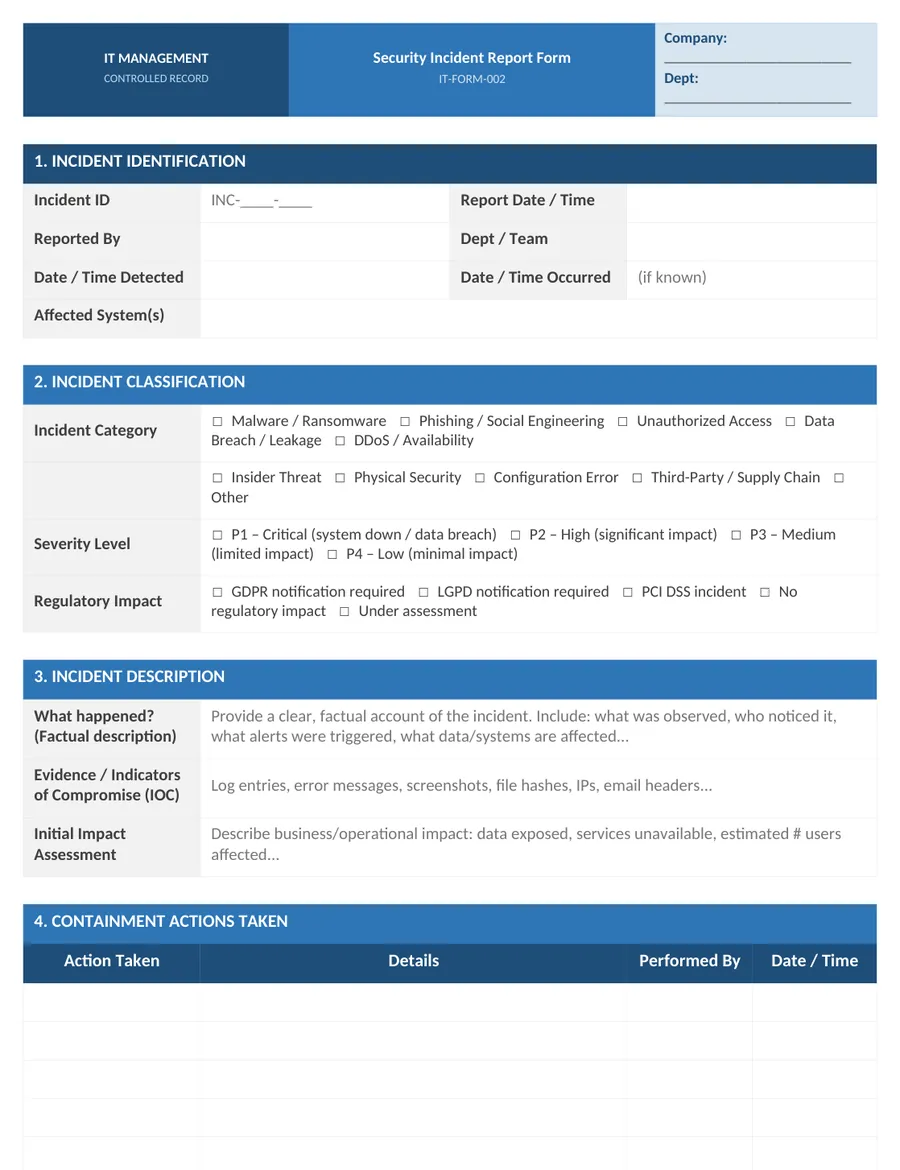
End-to-end incident lifecycle: P1–P4 classification, 10-category taxonomy, containment action log, root cause analysis (5 Whys / Fishbone), corrective actions, lessons learned, and regulatory notification tracker.
Full access lifecycle — new, modify, revoke, or temporary — with 4-level approval workflow (manager → resource owner → security → CISO), privileged access section, and user acknowledgment.
Risk & impact assessment, step-by-step implementation plan (6 rows), rollback plan with trigger criteria, test/success criteria, 5-role CAB approval table, and post-implementation review.
Scan identification, vulnerability register with CVSS scoring, remediation tracking with SLA targets (Critical ≤24h / High ≤7d / Medium ≤30d / Low ≤90d), and exception/risk acceptance section.
Asset registration through disposal: security controls (FDE, EDR, MDM, hardening), transfer log, maintenance history, and NIST 800-88 sanitization/certificate of destruction record.
NC identification (source, severity, standard reference), root cause analysis with method selection, corrective and preventive action plans with priority, and effectiveness verification + closure sign-off.
14-question security control assessment, contractual requirements verification (DPA, audit rights, sub-processor disclosure, incident SLA), Tier 1–4 risk classification, and approval decision with conditions.
RTO/RPO target vs. actual, step-by-step recovery log with pass/fail, data integrity verification (checksum, hash, record count, app test), outcome assessment, and corrective actions for failures.
Two-page form: 6 onboarding categories (hardware, network, email, apps, security, CMDB — 30 tasks) + 4 offboarding categories (access revocation, data, hardware return, security verification — 20 tasks).
Each form is directly linked to its corresponding SOP. When your team follows the Incident Response SOP, they fill IT-FORM-002. When a change is requested, IT-FORM-004 is opened alongside the Change Management SOP. Every form has a professional header, approval signature block, and revision history — generating the objective evidence your next audit requires.
These images were generated straight from the files you receive — nothing was mocked up or redrawn. Tap to enlarge.
SOPs define what to do. Forms capture what was done. These tools help you prove it's working — and improve it over time.
A complete ISMS monitoring workbook with 7 interconnected sheets. Track risks, incidents, KPIs, audit results, and corrective actions in one place. Over 2,000 formulas with auto-calculated risk scores, conformity rates, and resolution times.
A structured audit workbook covering all 93 ISO/IEC 27002:2022 Annex A controls across 4 categories. Executive summary with auto-calculated conformity rates, maturity scoring guide (1–5), and space for findings, corrective actions, and verification tracking.
Professionally structured, fully editable Word files with 15 standardized sections per SOP — plus forms and Excel tools.
💳 The platform will automatically convert the value to your local currency at checkout.
Secure payment via Hotmart. Immediate download after purchase.
Establish a complete documentation framework — procedures and records — for your department. Demonstrate compliance with structured, traceable SOPs backed by operational evidence.
Accelerate your ISO 27001 or ISO 20000 journey. Start with a solid foundation of SOPs and forms instead of building from zero — both the policies and the evidence trail.
Use as a baseline for client engagements. The linked SOP + form structure delivers professional results faster and impresses clients with a complete, integrated documentation system.
Skip the trial-and-error phase. Implement enterprise-grade processes and capture operational records from day one — without the enterprise budget or the consultant wait times.
Healthcare, fintech, government, pharma — industries where documentation isn't optional. Meet regulatory expectations with comprehensive IT procedures and audit-ready records for every key process.
Align IT documentation with your management system. Consistent format, standardized sections, and forms that generate the objective evidence your next audit requires — automatically.
40 SOPs. 10 operational forms. Two Excel tools. One investment that pays for itself in the first hour saved.
Get the Complete Kit — $49